

Lighter Pauses Withdrawals After $10.4 Million API Key Theft
The protocol says its smart contracts are intact, but it paused withdrawals as a precaution and activated Guardian mode. The stolen USDC was moved through ether and multiple wallets.
Key Takeaways
- Lighter paused withdrawals on Monday after a security issue involving a trader account led to the theft of $10.4 million in USDC.
- The protocol says the smart contracts were not affected and activated Guardian mode while the investigation was underway and a contract upgrade was being worked on.
- The LIT token fell more than 10% after the incident, and withdrawals were expected to reopen by the end of Monday.
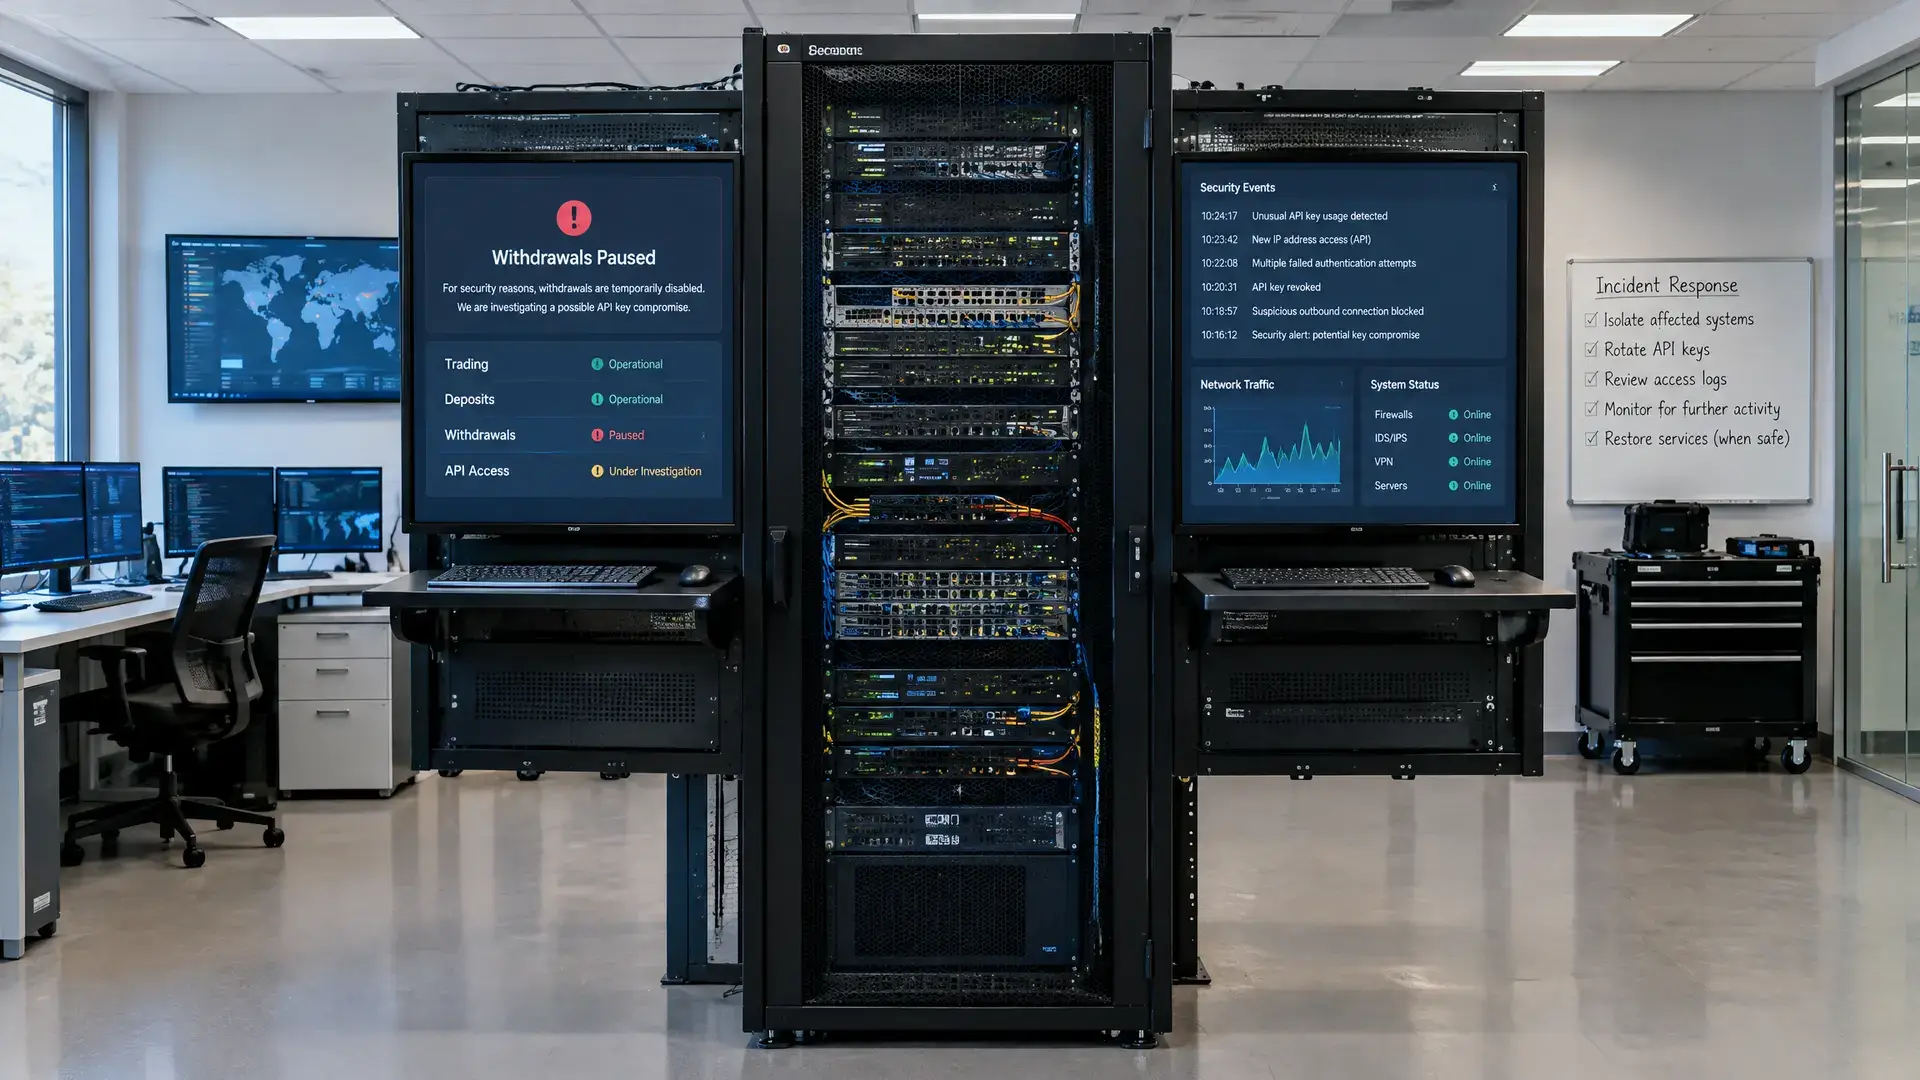
Lighter paused withdrawals on Monday after a security issue involving a trader account led to the theft of $10.4 million (€9.4 million) in USDC. Blockchain researchers tracked the stolen funds through ether and multiple wallets, while the DEX says the smart contracts themselves were not affected.
Investigation Into Leaked API Key
According to Lighter, the investigation points to a leaked API key from a specific trader. The protocol says its own smart contracts were not compromised, but it did keep withdrawals on hold while the security council worked on a contract upgrade. The platform also activated Guardian mode as a precaution and identified a wallet that is believed to belong to the attacker.
Bitquery traced a withdrawal of $10.39 million in USDC from Lighter's Ethereum contract to a wallet that converted the funds into ether within minutes. After that, 1,920 ETH, worth about $3.5 million (€3.2 million), was sent through 12 wallets to Hyperliquid, where the accounts bought XMR1, a token that refers to privacy coin Monero. Other researchers estimated the possible damage at $15.5 million (€14.1 million) across two market maker accounts, but Lighter has not confirmed that second withdrawal.
Withdrawals and Token Under Pressure
The native LIT token fell more than 10% after the incident to below $2.48 (€2.25). Later, the price recovered to $2.62 (€2.38), still nearly 9% lower over 24 hours. Lighter says withdrawals are expected to reopen by the end of Monday.
Why This Matters for DEX Users
The case shows how vulnerable a DEX can be when a trader's access key is misused, even when the underlying smart contracts stay intact. For European crypto users, that matters because more and more trading activity is happening onchain, and security on crypto platforms depends not just on code, but also on accounts and access rights. The timing is especially sensitive after the major Binance hack in October, which once again drew attention to the security of crypto platforms. Even with API keys from trading platforms, it was already clear how quickly account access can be cut off once a security risk is suspected.