Bitget Hack Puts NEAR Intents' 'Permissionless' Claim Under Pressure
NEAR Intents blocked more than $50 million in suspicious transfers from the Bitget hack. The move is fueling debate over what 'permissionless' means in DeFi and crosschain swaps.
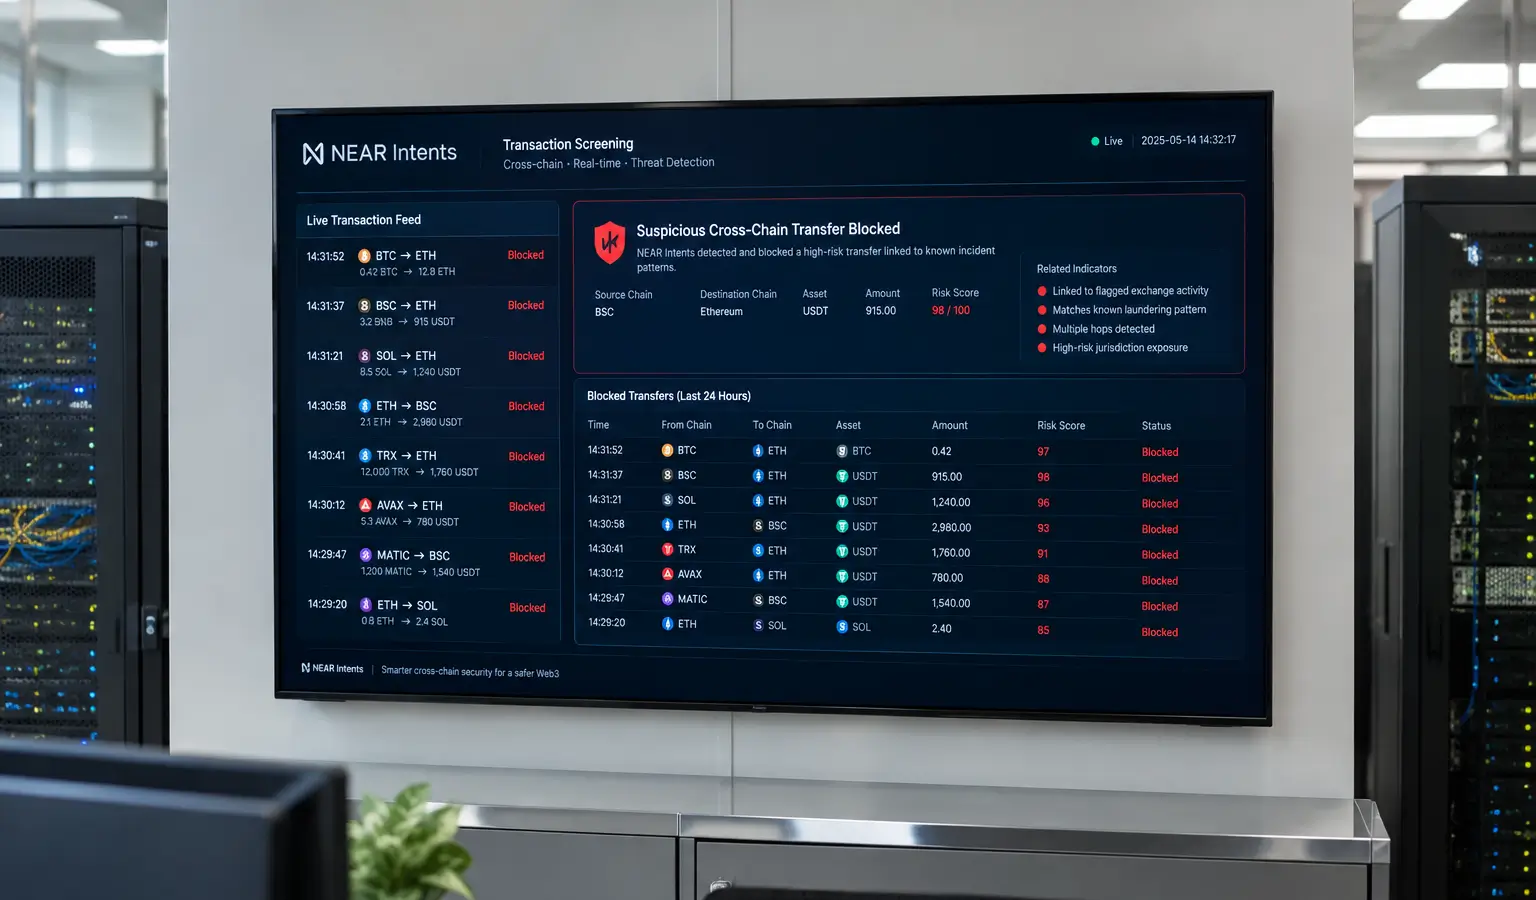
Key Takeaways
- NEAR Intents blocked more than $50 million in suspicious transfers from the Bitget hack through the SHIELD system.
- About $166,000 got through, while $503,000 was stopped and the rest is on hold for legal and recovery processing.
- The block sparked debate over whether NEAR Intents is still fully permissionless.
NEAR Intents is under the microscope after it blocked more than $50 million (€43.9 million) in suspicious transfers from the Bitget hack. The swap service calls itself permissionless and open, but stepped in when stolen funds tried to move through the protocol.
SHIELD Steps In
According to Alex Shevchenko, general manager of NEAR Intents, the attackers who drained $388 million (€341 million) from Bitget last week tried to move more than $50 million (€43.9 million) through the service. The SHIELD system blocked most of those attempts and stopped $503,000 (€442,100) halfway through. About $166,000 (€145,900) did get through, while the rest is now waiting on a legal and recovery process.
Shevchenko said duplicate attempts were removed from the count and that rejected funds later moved on through other providers. He said the amounts mentioned are estimates and could be off by about 10% from the actual total.
According to him, NEAR Intents normally processes more than $100 million (€87.9 million) in crosschain trading volume per day. In this case, it was only a small part of total activity, but it was money directly tied to a major hack.
Debate Over Permissionless
The move drew online criticism over whether a service that can stop transactions can still call itself permissionless. In crypto, permissionless means users can interact with a protocol without approval from a central party.
NEAR founder Illia Polosukhin responded that permissionless does not mean every app or liquidity provider has to process every transaction. In his view, it means no one needs permission to hold assets, transfer them, or deploy smart contracts on NEAR.
That nuance matters for European crypto readers because it shows how open access and abuse prevention increasingly have to coexist. With decentralized services, a security layer can absolutely affect how free a protocol feels in practice, without meaning it stops being open.
Broader Pattern After the Bitget Hack
Bitget disclosed the breach on September 24 after attackers bypassed security checks around exchange wallets. The company later said it had fixed the vulnerability, published attacker addresses, and offered bounties for help freezing or recovering funds.
Stablecoin issuers also stepped in. Circle and Tether have together already frozen about $320,000 (€281,200) in stablecoins linked to the hack. NEAR Intents is holding the intercepted funds for now while it waits for a legal and recovery process, but it has not yet explained who can authorize the release or how a wrongly flagged user gets their money back.
The debate fits into a broader trend in which protocols after major hacks are increasingly trying to block suspicious wallets, even when that clashes with their claim of full openness.