CZ Warns About AI Phishing, Bitcoin Core Updates Bug Policy
CZ points to AI-driven phishing and data leaks as an immediate risk, while Bitcoin Core is speeding up bug disclosures as vulnerabilities are found faster.
Key Takeaways
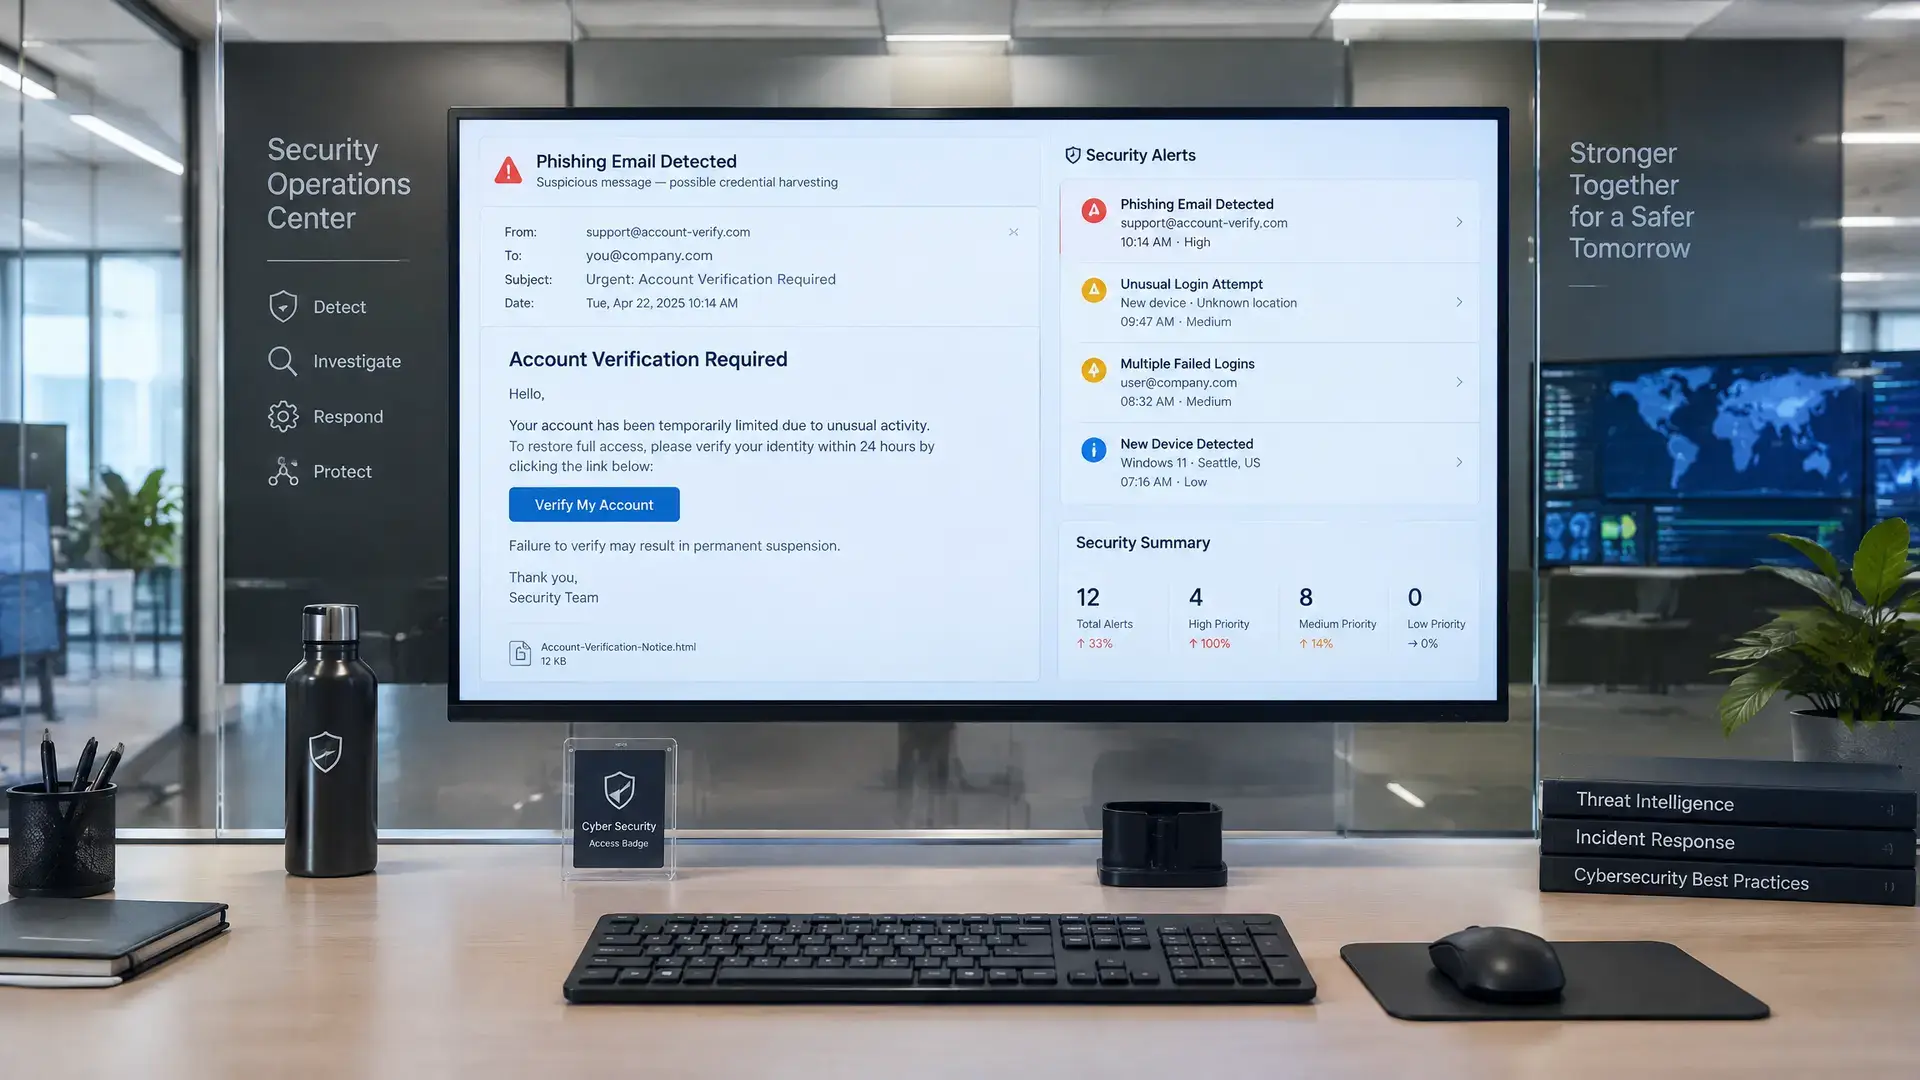
- CZ warns that AI can already cause damage through phishing and data leaks, without breaking Bitcoin cryptography.
- He says old leaked personal data and AI-written messages make scams more convincing for users.
- Bitcoin Core is updating its bug policy because AI makes vulnerabilities easier to spot and fixes need to be made public sooner.
Binance founder Changpeng Zhao warns that AI does not need to break Bitcoin cryptography to cause damage. According to him, the real risk is already in phishing and data leaks, while Bitcoin Core is also tightening its rules for reporting bugs because AI is making vulnerabilities easier to spot.
CZ Focuses on Phishing
Zhao, better known as CZ, wrote on X on October 23 that crypto encryption is not the weak link. He said banks and many internet services rely on weaker encryption than Bitcoin, and that those systems would therefore be hit sooner if AI ever really could crack code.
His main point, though, was that attackers can already do a lot today with old leaked personal data. That data gets combined with AI-written messages that look convincing and often seem to come from a real acquaintance or a trusted company. CZ ended his post with the familiar warning: “Stay SAFU!”
The warning lines up with broader concerns in the industry. AI makes phishing emails, fake messages, and other scams more believable, which means users can fall into traps faster without any complicated technical attack being needed.
Bitcoin Core Tightens the Rules
Bitcoin Core developer Antoine Poinsot announced a new security policy on Thursday on the Bitcoin Development Mailing List. The core of his message is that large language models can now find some bugs so quickly that long embargoes are no longer very useful. Because of that, fixes for easy-to-discover vulnerabilities will now be released as quickly as possible for all supported versions, along with the matching security advisories.
For other bugs, the severity-based system stays in place. Low-risk issues will be made public two weeks after a major release, while medium- and high-severity bugs will only be disclosed after the last affected version reaches end of life. Critical bugs will likely follow a separate process.
Why This Matters
For European crypto users, this shows that security is not just about the technology behind a blockchain, but also about the weakest link around accounts, messages, and data use. That matters for anyone who uses a crypto wallet or regularly works with exchanges and wallets. The combination of AI and leaked data can make scams more convincing, while developers also have to respond faster to software vulnerabilities.
Warnings about AI risks around wallets also show that the industry is mainly worried about abuse of existing accounts and addresses, not a direct breakthrough in cryptography.